


 |
市場調查報告書
商品編碼
2121201
雲端安全軟體:市場佔有率分析、產業趨勢與統計、成長預測(2026-2031)Cloud Security Software - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||

※ 本網頁內容可能與最新版本有所差異。詳細情況請與我們聯繫。
據 Mordor Intelligence 稱,2025 年雲端安全軟體市場價值為 501.1 億美元,預計到 2031 年將達到 1066 億美元,而 2026 年為 568.3 億美元,預測期(2026-2031 年)的複合年成長率為 13.4%。
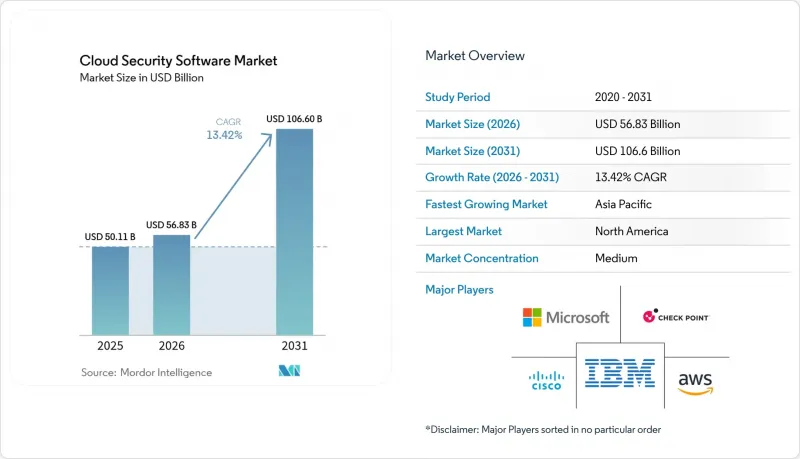
本報告按軟體(雲端 IAM、CASB、CNAPP/CWPP 等)、部署類型(公共雲端、私有雲端、混合/多重雲端)、組織規模(大型企業和中小企業 (SME))、最終用戶行業(銀行、金融服務和保險 (BFSI)、IT 和電信、醫療保健和生命科學等)以及地區進行分類。
全球雲端安全軟體市場趨勢與洞察
受監管產業中公共雲端採用率的快速成長
受監管企業正根據監管機構更新的雲端指南對其傳統架構進行現代化改造。聯邦金融監察委員會 (FFIEC) 目前強調即時第三方風險監控,促使銀行和保險公司實施自動化控制,以持續檢驗合規性證據。同樣,醫療保健機構也在製定現代化計畫,這些計劃不僅要滿足監管要求,還要與能夠帶來競爭優勢的安全認證保持一致。聯邦風險和授權管理計劃 (FedRAMP) 的改革進一步論證了雲端遷移的必要性,而這種採用預期也蔓延到了承包商和供應商。供應商正在積極回應,提供預先包裝的合規模板,以縮短部署時間,並將策略轉化為跨多重雲端環境的程式化安全措施。
多重雲端和混合雲端。
企業通常在 3.2 個雲端供應商上運行工作負載,這導致策略孤島和整合債務不斷增加。異質 API 和多樣化的安全模型推動了對集中式編排的需求,這種編排能夠標準化控制,而無需考慮底層編配。正因如此,能夠偵測容器和無伺服器函數中的配置錯誤和執行時期異常的雲端原生應用程式保護平台正日益受到關注。最初,企業採用多重雲端是為了分散風險,但現在,成本、效能和監管要求的差異促使他們依賴編配來維持營運的永續性。
與傳統安全架構相關的整合債務
隨著雲端控制與本地部署投資日益緊密地交織在一起,安全負責人正面臨工具重複和策略不一致的雙重挑戰。這些平行環境會掩蓋攻擊途徑並推高營運成本,尤其是當企業將零信任模型改造為中心輻射型網路時,問題更為突出。缺乏統一的遙測數據,威脅情報仍各自獨立,導致修復週期延長,安全投資報酬率降低。
細分市場分析
到 2025 年,雲端身分和存取管理 (IAM) 將佔據雲端安全軟體市場 34.42% 的佔有率,這反映了其在零信任架構實施中的基礎性作用。隨著企業優先採用最小權限策略以降低橫向遷移風險,該領域的強勁地位支撐著整個雲端安全軟體市場。同時,雲端原生應用程式保護平台和雲端工作負載保護平台預計到 2031 年將實現 14.12% 的複合年成長率,這反映了需要運行時保護的容器化工作負載的激增。這一成長與雲端存取安全仲介和漏洞掃描器整合到 DevSecOps 管線中,從而實現從開發到生產的持續評估密切相關。
整合日誌記錄的需求正在推動安全資訊和事件管理 (SIEM) 的現代化,相關平台利用機器學習來分析雲端規模的遙測數據,並縮短平均偵測時間 (MTD)。此外,正如 SEALSQ 的 Crystal Kyber 和 Crystal Dilithium 演示所展示的那樣,供應商正在進一步試驗抗量子演算法,這預示著密碼學邊界的長期演進。這些創新共同重新定義了類別邊界,促使平台供應商將相鄰功能整合到統一的套件中,以簡化採購和營運。
2025年,公共雲端仍將佔據雲端安全軟體市場64.85%的佔有率。這主要得益於超大規模資料中心業者雲端服務商在2025年高達2,150億美元的投資。光是亞馬遜就投資超過750億美元,用於增強原生保全服務和地理冗餘。儘管公共雲端具有規模經濟優勢,但隨著企業對工作負載可攜性、資料居住保障和成本最佳化的需求不斷成長,混合雲和多重雲端環境預計將以14.76%的複合年成長率(CAGR)成為成長最快的雲端環境。
混合環境日益複雜,對策略抽象的需求也隨之成長,安全提供者正致力於提供集中式控制面板,以便在 Kubernetes叢集、SaaS 應用和本地資產中強制執行統一的規則。儘管在擁有敏感知識產權和對延遲要求極高的工作負載的行業中,私有雲端的採用仍在繼續,但隨著合規性障礙的放寬,許多公司正將私有環境視為向公共雲端更廣泛遷移的過渡階段。
區域分析
預計到2025年,北美將維持40.95%的銷售佔有率,成為雲端安全軟體市場最大的區域市場佔有率。聯邦風險與授權管理計畫(FedRAMP)的現代化正在增強私人機構、承包商和高度監管產業對雲端控制的信心。同時,美國司法部的資料安全計畫正在對處理國際資料流量的電信業者引入新的合規要求,這催生了對自動化策略映射工具的需求,以協調重疊的規則集。
亞太地區是成長最快的地區,預計到2031年將以14.32%的複合年成長率成長,這主要得益於主權雲端指南、5G部署和廣泛的數位化。然而,嚴重的人才短缺正在威脅著實施進度。日本的技能短缺凸顯了人才培育的迫切性,促使大學、雲端服務供應商和安全性廠商開展合作,以擴大認證的取得途徑。中國正大力推動自主研發的安全架構以滿足主權要求,而印度則專注於低成本、擴充性的解決方案,以應對其多樣化的企業基礎設施。澳洲、紐西蘭和韓國正在利用先進的網路基礎設施部署即時威脅偵測平台,以確保金融交易和智慧工廠環境中的低延遲保護。
歐洲正在努力平衡創新與主權之間的關係。 《一般資料保護規則》(GDPR) 和不斷發展的網路與資訊安全指令正在塑造採購標準,優先考慮提供本地資料儲存選項和透明審計追蹤的供應商。德國在製造業領域主導新規的實施,而法國則投資建置國內託管的雲端區域,以支援關鍵基礎設施項目。脫歐後,英國正在製定自身的資料安全政策,同時保持足夠的協調性,以促進跨境資料傳輸。區域協調的努力正在簡化供應商進入流程,但各國指令本土化的進度不一,使得制定統一的部署策略仍十分複雜。
其他好處:
- Excel格式的市場預測(ME)表
- 3個月的分析師支持
目錄
第1章:引言
- 研究假設和市場定義
- 調查範圍
第2章:調查方法
第3章執行摘要
第4章 市場狀況
- 市場概覽
- 市場促進因素
- 公共雲端在受監管產業的應用正在迅速擴展。
- 多重雲端和混合雲端。
- 零信任架構的要求
- 人工智慧生成帶來的攻擊手法
- 網路保險保費優惠待遇
- 歐盟和亞太地區的自主雲計劃
- 市場限制因素
- 與傳統安全堆疊整合所面臨的挑戰
- 雲端原生工程師短缺
- 跨司法管轄區的合規衝突
- 影子IT和自備設備辦公室(BYOD)的持續趨勢
- 價值鏈分析
- 監管情勢和合規趨勢
- 技術展望
- 波特五力分析
第5章 市場規模與成長預測
- 軟體
- Cloud IAM
- CASB
- CNAPP/CWPP
- 脆弱性和風險管理
- 網路、電子郵件、DNS 安全
- SIEM 和日誌管理
- 部署模式
- 公共雲端
- 私有雲端
- 混合/多重雲端
- 按組織規模
- 大公司
- 中小企業
- 按最終用戶行業分類
- BFSI
- IT/通訊
- 醫療保健和生命科學
- 零售和消費品
- 製造業
- 其他
- 按地區
- 北美洲
- 美國
- 加拿大
- 墨西哥
- 歐洲
- 德國
- 英國
- 法國
- 義大利
- 西班牙
- 俄羅斯
- 其他歐洲國家
- 亞太地區
- 中國
- 日本
- 印度
- 韓國
- 澳洲和紐西蘭
- 其他亞太國家
- 南美洲
- 巴西
- 阿根廷
- 其他南美國家
- 中東和非洲
- 中東
- 沙烏地阿拉伯
- 阿拉伯聯合大公國
- 土耳其
- 其他中東國家
- 非洲
- 南非
- 奈及利亞
- 其他非洲國家
- 中東
- 北美洲
第6章 競爭情勢
- 市場集中度
- 策略趨勢
- 市佔率分析
- 公司簡介
- Palo Alto Networks
- Cisco Systems
- Fortinet
- Zscaler
- Check Point Software
- IBM
- Broadcom(CA Technologies)
- Microsoft
- Trend Micro
- Okta
- CrowdStrike
- Rapid7
- Amazon Web Services(Security services)
- Google Cloud Security
- HPE(Aruba)
- Proofpoint
- Sophos
- Imperva
- Netskope
- Qualys
- F5 Networks
第7章 市場機會與未來展望
According to Mordor Intelligence, the cloud security software market size was valued at USD 50.11 billion in 2025 and estimated to grow from USD 56.83 billion in 2026 to reach USD 106.6 billion by 2031, at a CAGR of 13.42% during the forecast period (2026-2031).
This report is Segmented by Software (Cloud IAM, CASB, CNAPP / CWPP, and More), Deployment Mode (Public Cloud, Private Cloud, and Hybrid / Multi-Cloud), Organization Size (Large Enterprises and Small and Medium Enterprises (SMEs)), End-User Industry (BFSI, IT and Telecom, Healthcare and Life-Sciences, and More), and Geography.
Global Cloud Security Software Market Trends and Insights
Fast-growing Public-cloud Adoption Among Regulated Industries
Regulated enterprises are re-tooling legacy architectures as supervisory bodies update cloud guidance. The Federal Financial Institutions Examination Council now stresses real-time third-party risk monitoring, prompting banks and insurers to adopt automated controls that verify compliance evidence continuously. Healthcare providers likewise align modernization plans with security certifications that deliver competitive benefit rather than mere regulatory box-ticking. Federal Risk and Authorization Management Program reforms further legitimize cloud migrations, cascading adoption expectations across contractors and suppliers. Vendors respond with pre-packaged compliance templates that shorten onboarding times and translate policy into programmatic guardrails across multi-cloud estates.
Surge in Multi-cloud and Hybrid-cloud Complexity
Enterprises typically run workloads on 3.2 cloud providers, multiplying policy silos and integration debt. Disparate APIs and variable security models fuel demand for centralized orchestration able to normalize controls independent of underlying infrastructure. Cloud-native application protection platforms thus gain favor by detecting misconfigurations and runtime anomalies across containers and serverless functions. Organizations originally pursued multi-cloud for diversification but now rely on orchestration to maintain operational viability as cost, performance, and jurisdictional requirements diverge.
Integration Debt with Legacy Security Stacks
Security leaders grapple with duplicated tooling and inconsistent policies as cloud controls overlay on-premises investments. Parallel environments obscure attack paths and inflate operating costs, especially when organizations retrofit zero-trust models onto hub-and-spoke networks. Without unified telemetry, threat intelligence remains siloed, and remediation cycles extend, undermining return on security spend.
Other drivers and restraints analyzed in the detailed report include:
- Zero-trust Architecture Mandates
- Generative-AI-driven Threat Vectors
- Cloud-native Skills Shortage
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Cloud Identity and Access Management accounted for a 34.42% cloud security software market share in 2025, reflecting its cornerstone role in zero-trust rollouts. The segment's entrenched status underpins the broader cloud security software market as organizations prioritize least-privilege policies to mitigate lateral movement risks. Simultaneously, Cloud-Native Application Protection Platforms and Cloud Workload Protection Platforms achieve a 14.12% CAGR through 2031, mirroring the proliferation of containerized workloads that require runtime safeguards. Their ascent joins Cloud Access Security Brokers and vulnerability scanners that integrate within DevSecOps pipelines, offering continuous assessment across development and production.
Demand for unified logging drives Security Information and Event Management modernization, with platforms leveraging machine learning to parse cloud-scale telemetry and accelerate mean-time-to-detect. Vendors further experiment with quantum-resistant algorithms, as demonstrated by SEALSQ's Crystal Kyber and Crystal Dilithium showcase, signaling the long-term evolution of encryption boundaries. These innovations collectively reshape category borders, encouraging platform vendors to fold adjacent capabilities into consolidated suites for simplified procurement and operations.
Public cloud retained 64.85% share of the cloud security software market size in 2025, buoyed by hyperscaler investments that reached USD 215 billion in 2025. Amazon alone allocated more than USD 75 billion, augmenting native security services and geographic redundancy. Despite public cloud scale advantages, hybrid and multi-cloud environments post the fastest 14.76% CAGR as enterprises seek workload portability, data residency assurance, and cost optimization.
Hybrid complexity magnifies the need for policy abstraction, prompting security providers to offer central dashboards that push uniform rules across Kubernetes clusters, SaaS applications, and on-premises assets. Private cloud adoption persists among industries with sensitive intellectual property or latency-critical workloads, though many treat private environments as transitional waypoints toward broader public adoption once compliance hurdles ease.
Complete Report Scope:
- By Software
- Cloud IAM
- CASB
- CNAPP / CWPP
- Vulnerability and Risk Management
- Web, Email and DNS Security
- SIEM and Log Management
- By Deployment Mode
- Public Cloud
- Private Cloud
- Hybrid / Multi-Cloud
- By Organization Size
- Large Enterprises
- Small and Medium Enterprises (SMEs)
- By End-User Industry
- BFSI
- IT and Telecom
- Healthcare and Life-Sciences
- Retail and Consumer Goods
- Manufacturing
- Others
- By Geography
- North America
- United States
- Canada
- Mexico
- Europe
- Germany
- United Kingdom
- France
- Italy
- Spain
- Russia
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- Australia and New Zealand
- Rest of Asia-Pacific
- South America
- Brazil
- Argentina
- Rest of South America
- Middle East and Africa
- Middle East
- Saudi Arabia
- United Arab Emirates
- Turkey
- Rest of Middle East
- Africa
- South Africa
- Nigeria
- Rest of Africa
- Middle East
- North America
Geography Analysis
North America retained a 40.95% revenue share in 2025, signifying the largest regional slice of the cloud security software market. Federal Risk and Authorization Management Program modernization boosts confidence in cloud controls across civilian agencies, contractors, and heavily regulated industries. Concurrently, the U.S. Department of Justice Data Security Program introduces fresh compliance layers for telecommunications firms handling foreign data traffic, generating opportunities for automated policy-mapping tools that reconcile overlapping rule sets.
Asia-Pacific is the fastest-growing territory with a 14.32% CAGR through 2031, underpinned by sovereign-cloud directives, 5G rollout, and broad-scale digitization. Yet acute talent shortages threaten execution timelines. Japan's skills deficit underscores the training imperative, spurring partnerships between universities, cloud providers, and security vendors to expand certification access. China advances domestically sourced security stacks to meet sovereignty mandates, whereas India emphasizes low-cost, scalable solutions to service a diverse enterprise base. Australia, New Zealand, and South Korea leverage advanced network infrastructure to adopt real-time threat detection platforms that ensure low-latency protection for financial trading and smart-factory environments.
Europe navigates the delicate balance between innovation and sovereignty. General Data Protection Regulation and the evolving Network and Information Security Directive shape procurement criteria that favor providers offering data-localization options and transparent audit trails. Germany leads adoption in manufacturing, while France invests in nationally hosted cloud zones to underpin critical infrastructure projects. Post-Brexit, the United Kingdom crafts its own data security stance yet aligns closely enough to facilitate cross-border transfers. Regional harmonization efforts simplify vendor entry, although divergent national timelines for directive transposition continue to complicate uniform rollout strategies.
- Palo Alto Networks
- Cisco Systems
- Fortinet
- Zscaler
- Check Point Software
- IBM
- Broadcom (CA Technologies)
- Microsoft
- Trend Micro
- Okta
- CrowdStrike
- Rapid7
- Amazon Web Services (Security services)
- Google Cloud Security
- HPE (Aruba)
- Proofpoint
- Sophos
- Imperva
- Netskope
- Qualys
- F5 Networks
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Fast-growing public-cloud adoption among regulated industries
- 4.2.2 Surge in multi-cloud and hybrid-cloud complexity
- 4.2.3 Zero-trust architecture mandates
- 4.2.4 Generative-AI-driven threat vectors
- 4.2.5 Cyber-insurance premium incentives
- 4.2.6 Sovereign-cloud initiatives in EU and APAC
- 4.3 Market Restraints
- 4.3.1 Integration debt with legacy security stacks
- 4.3.2 Cloud-native skills shortage
- 4.3.3 Compliance conflicts across jurisdictions
- 4.3.4 Persistent shadow-IT and BYOD behaviour
- 4.4 Value Chain Analysis
- 4.5 Regulatory and Compliance Landscape
- 4.6 Technological Outlook
- 4.7 Porter's Five Forces Analysis
- 4.7.1 Bargaining Power of Suppliers
- 4.7.2 Bargaining Power of Buyers
- 4.7.3 Threat of New Entrants
- 4.7.4 Threat of Substitutes
- 4.7.5 Intensity of Competitive Rivalry
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Software
- 5.1.1 Cloud IAM
- 5.1.2 CASB
- 5.1.3 CNAPP / CWPP
- 5.1.4 Vulnerability and Risk Management
- 5.1.5 Web, Email and DNS Security
- 5.1.6 SIEM and Log Management
- 5.2 By Deployment Mode
- 5.2.1 Public Cloud
- 5.2.2 Private Cloud
- 5.2.3 Hybrid / Multi-Cloud
- 5.3 By Organization Size
- 5.3.1 Large Enterprises
- 5.3.2 Small and Medium Enterprises (SMEs)
- 5.4 By End-User Industry
- 5.4.1 BFSI
- 5.4.2 IT and Telecom
- 5.4.3 Healthcare and Life-Sciences
- 5.4.4 Retail and Consumer Goods
- 5.4.5 Manufacturing
- 5.4.6 Others
- 5.5 By Geography
- 5.5.1 North America
- 5.5.1.1 United States
- 5.5.1.2 Canada
- 5.5.1.3 Mexico
- 5.5.2 Europe
- 5.5.2.1 Germany
- 5.5.2.2 United Kingdom
- 5.5.2.3 France
- 5.5.2.4 Italy
- 5.5.2.5 Spain
- 5.5.2.6 Russia
- 5.5.2.7 Rest of Europe
- 5.5.3 Asia-Pacific
- 5.5.3.1 China
- 5.5.3.2 Japan
- 5.5.3.3 India
- 5.5.3.4 South Korea
- 5.5.3.5 Australia and New Zealand
- 5.5.3.6 Rest of Asia-Pacific
- 5.5.4 South America
- 5.5.4.1 Brazil
- 5.5.4.2 Argentina
- 5.5.4.3 Rest of South America
- 5.5.5 Middle East and Africa
- 5.5.5.1 Middle East
- 5.5.5.1.1 Saudi Arabia
- 5.5.5.1.2 United Arab Emirates
- 5.5.5.1.3 Turkey
- 5.5.5.1.4 Rest of Middle East
- 5.5.5.2 Africa
- 5.5.5.2.1 South Africa
- 5.5.5.2.2 Nigeria
- 5.5.5.2.3 Rest of Africa
- 5.5.5.1 Middle East
- 5.5.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global level Overview, Market level overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share for key companies, Products and Services, and Recent Developments)
- 6.4.1 Palo Alto Networks
- 6.4.2 Cisco Systems
- 6.4.3 Fortinet
- 6.4.4 Zscaler
- 6.4.5 Check Point Software
- 6.4.6 IBM
- 6.4.7 Broadcom (CA Technologies)
- 6.4.8 Microsoft
- 6.4.9 Trend Micro
- 6.4.10 Okta
- 6.4.11 CrowdStrike
- 6.4.12 Rapid7
- 6.4.13 Amazon Web Services (Security services)
- 6.4.14 Google Cloud Security
- 6.4.15 HPE (Aruba)
- 6.4.16 Proofpoint
- 6.4.17 Sophos
- 6.4.18 Imperva
- 6.4.19 Netskope
- 6.4.20 Qualys
- 6.4.21 F5 Networks
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-space and Unmet-need Assessment

 2026年全球國防雲市場報告
 銀行業雲端安全:市場佔有率分析、產業趨勢與統計及成長預測(2026-2031 年)製造業雲端安全:市場佔有率分析、產業趨勢與統計及成長預測(2026-2031 年)
 雲端安全市場預測至 2034 年—按組件、部署模式、組織規模、安全類型、產業和地區分類的全球分析
 雲端安全市場:2026-2032年全球市場預測(依產品、服務模式、安全類型、部署模式、產業及組織規模分類)
 2026-2034年全球雲端安全市場規模、佔有率、趨勢和成長分析報告
 雲端安全市場規模、佔有率和趨勢分析報告:按組件、部署類型、企業規模、最終用途、地區和細分市場預測(2026-2033 年)能源產業雲端安全:市場佔有率分析、產業趨勢與統計及成長預測(2026-2031 年)
 雲端原生安全平台市場:按組件、組織規模、應用、安全類型、國家及地區分類-全球產業分析、市場規模、市場佔有率及2026年至2033年預測
 全球雲端安全市場(至 2031 年):按類型(CNAPP(CWPP、CSPM、CIEM、CDR、KSPM、IAC 安全)、CASB、分析與監控)、部署類型(私人、公有、混合)和產業(醫療保健、零售與電子商務、媒體與娛樂)分類