


 |
市場調查報告書
商品編碼
2157044
雲端事件回應服務:市場佔有率分析、產業趨勢與統計資料、成長預測(2026-2031 年)Cloud Incident Response Services - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||

※ 本網頁內容可能與最新版本有所差異。詳細情況請與我們聯繫。
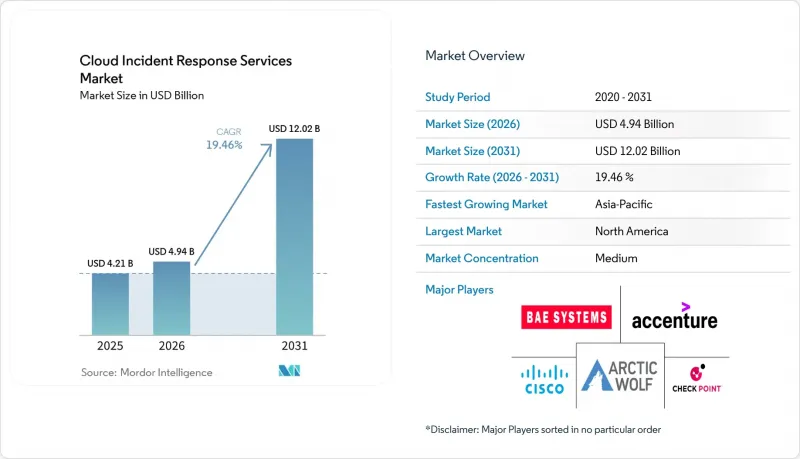
根據 Mordor Intelligence 預測,雲端事件回應服務市場規模將從 2025 年的 42.1 億美元和 2026 年的 49.4 億美元成長到 2031 年的 120.2 億美元,2026 年至 2031 年的年複合成長率(CAGR)為 19.46%。
全球雲端事件回應服務市場趨勢與洞察
雲端身分和 API 的濫用日益增多
由於雲端安全漏洞通常始於憑證或權限洩露,因此身分相關的調查在固定價格事件回應預算中所佔比例越來越大。由於身分控制會影響整個攻擊向量的存取權限,因此回應團隊必須對身分控制進行深入審查,而不僅限於初始入口點。攻擊者可以利用被盜用的帳戶存取正常的雲端服務,同時逃避對可疑活動的偵測。事件回應團隊必須重建授權鏈、令牌歷史記錄、服務帳戶權限路徑以及存取策略變更。這需要了解身分如何在雲端平台和相關應用程式中實現的專家。在雲端事件回應服務市場中,擁有雲端身分取證專業技能的供應商,而非僅僅照搬本地環境通用回應方案的供應商,具有顯著優勢。
AI加速的攻擊者策略
2025年,人工智慧將成為實際攻擊活動中不可或缺的一部分,這將改變調查和遏制攻擊的時間。 2025年6月,GoogleMandiant發現了名為「PROMPTFLUX」的工具,該工具透過查詢Gemini API定期重寫VBScript原始碼,產生多型行為。攻擊自動化可以縮短從入侵到橫向移動和資料竊取的時間。此外,僅靠靜態規則難以偵測不斷變化的惡意活動。這種情況使得自動化分類系統的需求日益成長,該系統能夠在分析人員審查每個警報之前採取行動。此外,能夠將檢測和遏制整合到單一營運模式中的事件回應服務提供者的需求也在不斷成長。
由於日誌配置錯誤,導致證據缺失。
雲端系統高度依賴遙測技術,但糟糕的日誌配置往往會導致調查過程中關鍵證據的缺失。 Palo Alto Networks 在 2025 年全球事件回應報告中指出,在近一半的雲端安全漏洞事件中,攻擊者利用了配置錯誤的存取和身分控制。企業可能會為了控制儲存成本而限制細粒度的 API 日誌記錄,但這會導致遺失識別攻擊者路徑和漏洞範圍所需的記錄。預設設定可能不足以應對此類情況,尤其是在容器和無伺服器工作負載中,因為這些工作負載的事件量往往巨大,而保留期限卻很短。即使聘請了高級服務商或使用自動化腳本,也無法彌補從未收集到的來源資訊。對於那些沒有建立完善日誌環境的企業而言,這種限制可能會降低雲端事件回應服務市場的有效性。
細分市場分析
預計從2026年到2031年,託管偵測與回應 (MDR) 的複合年成長率將達到23.17%,成為成長最快的服務類型。其固定費率合約模式將持續監控、威脅搜尋和回應執行整合到一份合約中。這種結構避免了在安全漏洞發生後,買家尋求緊急援助時可能出現的採購延誤。 2026年3月,CrowdStrike推出了“Agentic MDR”,它將自主AI代理與Falcon Complete分析師相結合,以實現繁瑣安全任務的自動化。這項服務體現了加強檢測和遏制之間協調的重要性日益凸顯。雲端事件回應服務市場中託管偵測與回應 (MDR) 的需求主要來自那些無法維持自身全天候威脅情報和回應團隊的組織。
2025年,遏制和緩解措施佔服務類型支出的32.86%,是該領域雲端事件回應服務中佔比最大的部分。在確認發生安全漏洞後,防止事件升級仍是首要的營運任務。在遏制措施之後,通常會進行調查和數位取證,因為事件回應負責人需要找出事件經過並保存證據。隨後的糾正措施和恢復工作著重於恢復服務、糾正控制措施以及降低事件再次發生的可能性。其他服務配置包括雲端身分管理合約和基於結果的合約。因此,這種服務組合反映了許多組織管理雲端安全事件的順序。
預計到 2025 年,公共雲端在部署環境中的支出佔比將達到 54.29%,並且從 2026 年到 2031 年的複合年成長率將達到 22.86%。這反映出企業工作負載和安全事件在公共雲端平台上的集中度日益提高。 AWS、Microsoft Azure 和 Google Cloud 提供的遙測資料擴大被設計用於由專業的事件回應平台進行收集和分析。 2026 年 4 月,CrowdStrike 將其即時雲端偵測和回應能力擴展到了 Google Cloud。此次擴展實現了跨分散式環境的統一響應。因此,在這種部署環境下,公共雲端佔據了雲端事件回應服務市場的最大佔有率。
私有雲、混合雲和多重雲端環境各自需要不同的證據收集技術和回應負責人的專業知識。在混合環境中,團隊需要關聯本地和雲端記錄,這些記錄可能遵循不同的模式和保留期限。在多重雲端環境中,由於帳戶和令牌可能跨越雲端邊界,因此會面臨身分和權限方面的挑戰。 IBM 的研究表明,識別和控制混合雲和多重雲端環境中的安全漏洞比在單一環境中需要更長的時間。各組織正在投資自動化證據保存技術,以便在受影響的實例因擴展策略而關閉之前捕獲不穩定狀況。這些情況凸顯了部署專業知識在雲端事件回應服務市場的重要性。
區域分析
到2025年,北美將佔據全球雲端事件回應服務市場36.74%的佔有率,成為該地區最大的市場。企業雲端的普及、成熟的供應商網路以及對事件應變準備工作的投入,都支撐了這一地位。美國證券交易委員會(SEC)的網路安全資訊揭露要求,促使董事會更加重視事件的重要性評估和緊急應變計畫。此外,受加拿大隱私權保護框架和墨西哥對數位基礎設施安全的重視,市場需求也正在向美國以外的地區擴展。買家越來越傾向於主動、預先安排的回應支持,而不是在事件發生後才進行緊急採購。
預計亞太地區在2026年至2031年間將以24.63%的複合年成長率成長,成為所有地區中成長最快的地區。雲端運算的普及和政府網路安全要求的提高,推動了全部區域對主動響應服務的需求成長。印度的資料保護框架和全球交付中心的存在,凸顯了跨國公司處理敏感資訊的重要性。新加坡和澳洲也透過雲端配置和資料外洩回應要求影響採購趨勢。能夠支持本地證據保留要求和監管合規的供應商,將更有利於滿足該地區的需求。
在歐洲,DORA、NIS2 和 GDPR 的要求正在重塑市場格局,尤其是在德國、英國、法國和比荷盧經濟聯盟等金融中心。南美洲的市場基數小規模,目前主要集中在巴西和阿根廷的金融機構和政府機構。沙烏地阿拉伯和阿拉伯聯合大公國對關鍵基礎設施營運商的事件回應計畫的要求日益提高。在非洲,南非和奈及利亞的金融服務和電信公司在採用這些計畫方面處於領先地位,但由於缺乏供應商和專業知識,短期進展有限。
其他好處:
- Excel格式的市場預測(ME)表
- 3個月的分析師支持
目錄
第1章:引言
- 研究假設和市場定義
- 調查範圍
第2章:調查方法
第3章執行摘要
第4章 市場狀況
- 市場概覽
- 市場促進因素
- 雲端身分和 API 的濫用現像日益增加。
- 多重雲端和臨時工作負載的複雜性
- 監理與網路保險合規義務
- 雲取證領域專家短缺
- 人工智慧加速了攻擊者的戰術。
- 機器可讀證據和自動化隔離
- 市場限制因素
- 由於日誌設定不正確,導致證據缺失。
- 數據主權和跨境證據限制
- 工具集碎片化與責任分類不明確
- 調查期間工作量的暫時波動
- 宏觀經濟因素的影響
- 優先考慮公司安全預算
- 網路保險保費設定和免賠額變更
- IT現代化與雲端投資的週期
- 價值供應鏈分析
- 監理情勢
- NIST SP 800-61 與 NIST 網路安全框架
- ISO/IEC 27001、SOC 2 與 CIS 控制
- GDPR、CCPA/CPRA 和區域隱私要求
- NIS2、DORA 和特定產業資訊通訊技術韌性法規
- HIPAA、PCI DSS、SEC揭露和資料外洩通知截止日期
- 證據儲存、法律保存義務和跨境資料傳輸
- 技術展望
- 雲端原生取證和基於 API 的證據收集
- ID、存取權限和令牌取證
- 容器、Kubernetes 和無伺服器運算的研究
- 人工智慧驅動的分類和時間軸重建
- 自動隔離、憑證撤銷和金鑰輪換
- 不可竄改的證據庫和密碼完整性
- 雲沙箱、數位孿生和欺騙
- 波特五力分析
第5章 市場規模與成長預測
- 按服務類型
- 調查和數位取證
- 遏制與緩解
- 修復和恢復
- 託管偵測與回應
- 其他服務類型
- 透過雲端環境
- 公共雲端
- 私有雲端
- 混合雲端
- 多重雲端
- 按組織規模
- 大公司
- 小型企業
- 按行業分類
- 政府和公共行政
- 工業製造
- 零售與電子商務
- 運輸/物流
- 能源公用事業
- 石油和天然氣
- 資訊科技/通訊
- 媒體與娛樂
- 教育和研究機構
- 醫療保健和生命科學
- 銀行、金融服務和保險(BFSI)
- 其他工業部門
- 按地區
- 北美洲
- 美國
- 加拿大
- 墨西哥
- 南美洲
- 巴西
- 阿根廷
- 其他南美國家
- 歐洲
- 德國
- 英國
- 法國
- 義大利
- 西班牙
- 其他歐洲國家
- 亞太地區
- 中國
- 日本
- 印度
- 韓國
- 澳洲
- 其他亞太國家
- 中東
- 沙烏地阿拉伯
- 阿拉伯聯合大公國
- 其他中東國家
- 非洲
- 南非
- 奈及利亞
- 其他非洲國家
- 北美洲
第6章 競爭情勢
- 市場集中度
- 策略趨勢
- 市佔率分析
- 公司簡介
- Accenture plc
- Arctic Wolf Networks, Inc.
- BAE Systems plc
- Check Point Software Technologies Ltd.
- Cisco Systems, Inc.
- CrowdStrike Holdings, Inc.
- Deloitte Touche Tohmatsu Limited
- Ernst & Young Global Limited
- Google LLC, Mandiant
- International Business Machines Corporation
- Kaspersky Lab
- KPMG International Limited
- Microsoft Corporation
- NCC Group plc
- NTT DATA Corporation
- Optiv Security Inc.
- Palo Alto Networks, Inc.
- PricewaterhouseCoopers International Limited
- Rapid7, Inc.
- Secureworks Corp.
- SentinelOne, Inc.
- Sophos Limited
第7章 市場機會與未來展望
According to Mordor Intelligence, the cloud incident response services market size is projected to expand from USD 4.21 billion in 2025 and USD 4.94 billion in 2026 to USD 12.02 billion by 2031, registering a CAGR of 19.46% between 2026 to 2031.
Global Cloud Incident Response Services Market Trends and Insights
Rising Cloud Identity and API Abuse
Identity-related investigations are taking a larger share of response retainer budgets because cloud breaches often begin with compromised credentials or permissions. Identity controls influence access throughout the attack path, so response teams must examine them beyond the first point of entry. Compromised accounts can allow an attacker to use ordinary cloud services while avoiding attention from controls that rely on unfamiliar behavior. Response teams must reconstruct consent chains, token histories, service-account privilege paths, and changes to access policies. That work requires specialists who understand how identity is implemented across cloud platforms and connected applications. The cloud incident response services market favors providers with dedicated cloud identity forensic skills instead of general response playbooks adapted from on-premises environments.
AI-Accelerated Attacker Tradecraft
AI became part of operational attack activity during 2025, which changed the time available for investigation and containment. Google Mandiant identified PROMPTFLUX in June 2025, a tool that queried the Gemini API to rewrite its VBScript source code regularly and create polymorphic behavior. Attack automation can reduce the time between access, lateral movement, and data theft. It also makes repeated variations of malicious activity harder to detect with static rules alone. These conditions increase the need for automated triage that can act before analysts review each alert. They increase demand for response providers that connect detection and containment in a single operating model.
Evidence Gaps From Logging Misconfiguration
Cloud response depends on complete telemetry, yet logging configurations often leave important evidence unavailable at the time of an investigation. Palo Alto Networks reported that attackers exploited misconfigured access and identity controls in nearly half of the cloud breaches covered by its 2025 global incident response report. Organizations may limit detailed API logging to control storage costs, but this can remove the records needed to establish an attacker's path and the scope of a breach. Default settings can be particularly inadequate for container and serverless workloads, where event volumes are high and retention periods may be short. Retainers and automated playbooks cannot replace source information that was never captured. This constraint can reduce the effectiveness of the cloud incident response services market for organizations that have not prepared their logging environment.
Other drivers and restraints analyzed in the detailed report include:
- Regulatory and Cyber-Insurance Response Obligations
- Multi-Cloud and Ephemeral Workload Complexity
- Data Sovereignty and Cross-Border Evidence Restrictions
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Managed detection and response is projected to expand at a 23.17% CAGR during 2026-2031, making it the fastest-growing service type. Its retainer model combines continuous monitoring, threat hunting, and response execution under one agreement. This structure avoids procurement delays that can occur when a buyer seeks emergency assistance after a breach. CrowdStrike introduced Agentic MDR in March 2026, combining autonomous AI agents with Falcon Complete analysts to automate high-friction security work. The offering reflects the growing value placed on a closer connection between detection and containment. The cloud incident response services market size for managed detection and response is supported by organizations that cannot maintain their own round-the-clock threat intelligence and response teams.
Containment and mitigation accounted for 32.86% of service-type spending in 2025, the largest share of Cloud incident response services within this segmentation. Stopping the spread of an incident remains the immediate operating priority after a breach is confirmed. Investigation and digital forensics commonly follow containment because responders need to establish what occurred and preserve evidence. Remediation and recovery then focus on restoring services, correcting controls, and reducing the chance of recurrence. Other service configurations include cloud identity retainers and outcome-based arrangements. The service mix, therefore, reflects the order in which many organizations manage a cloud security incident.
Public cloud held 54.29% of deployment-context spending in 2025 and is projected to expand at a 22.86% CAGR during 2026-2031. This position reflects the concentration of enterprise workloads and security events in public cloud platforms. AWS, Microsoft Azure, and Google Cloud provide telemetry that specialized response platforms are increasingly designed to collect and analyze. CrowdStrike extended its real-time cloud detection and response capabilities to Google Cloud in April 2026. The expansion supports a unified response across distributed environments. Public cloud, therefore, holds the leading market share in cloud incident response services for the deployment context.
Private, hybrid, and multi-cloud environments require different evidence collection methods and responder expertise. Hybrid deployments require teams to correlate on-premises and cloud records that may use different schemas and retention periods. Multi-cloud estates add identity and permission challenges because accounts and tokens can span cloud boundaries. IBM found that hybrid and multi-cloud breaches took longer to identify and contain than breaches in a single environment. Organizations are investing in automated evidence preservation to capture the volatile state before scaling policies remove affected instances. These conditions keep specialized deployment knowledge important across the cloud incident response services market.
Complete Report Scope:
- By Service Type
- Investigation and Digital Forensics
- Containment and Mitigation
- Remediation and Recovery
- Managed Detection and Response
- Other Service Types
- By Cloud Environment
- Public Cloud
- Private Cloud
- Hybrid Cloud
- Multi-Cloud
- By Organization Size
- Large Enterprises
- Small and Medium Enterprises
- By Industry Vertical
- Government and Public Administration
- Industrial Manufacturing
- Retail and E-Commerce
- Transportation and Logistics
- Energy and Utilities
- Oil and Gas
- IT and Telecommunication
- Media and Entertainment
- Education and Research Institutions
- Healthcare and Life Sciences
- Banking, Financial Services, and Insurance (BFSI)
- Other Industry Verticals
- By Geography
- North America
- United States
- Canada
- Mexico
- South America
- Brazil
- Argentina
- Rest of South America
- Europe
- Germany
- United Kingdom
- France
- Italy
- Spain
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- Australia
- Rest of Asia-Pacific
- Middle East
- Saudi Arabia
- United Arab Emirates
- Rest of Middle East
- Africa
- South Africa
- Nigeria
- Rest of Africa
- North America
Geography Analysis
North America held 36.74% of the global cloud incident response services market in 2025, the largest regional share. Enterprise cloud adoption, established provider networks, and response-readiness spending underpin its position. SEC cybersecurity disclosure requirements have increased board attention to materiality assessments and prepared response programs. Canada's privacy framework and Mexico's focus on digital infrastructure security extend demand beyond the United States. Buyers increasingly seek pre-arranged response support instead of emergency sourcing after an event.
Asia-Pacific is forecast to expand at a 24.63% CAGR during 2026-2031, the fastest regional rate. Cloud adoption and government cybersecurity requirements are expanding the need for prepared response services across the region. India's data protection framework and global delivery centers increase the importance of handling sensitive multinational information. Singapore and Australia are also influencing procurement through cloud configuration and breach-response requirements. Providers that can support local evidence residency and regulatory response are well placed to serve this regional demand.
Europe is shaped by DORA, NIS2, and GDPR requirements, especially in financial centers across Germany, the United Kingdom, France, and Benelux. South America is developing from a smaller base, with demand in Brazil and Argentina centered on financial institutions and government entities. Saudi Arabia and the United Arab Emirates have increased incident-planning requirements for critical infrastructure operators. South Africa and Nigeria lead African adoption among financial services and telecommunications firms, although provider availability and specialized skills limit near-term progress.
- Accenture plc
- Arctic Wolf Networks, Inc.
- BAE Systems plc
- Check Point Software Technologies Ltd.
- Cisco Systems, Inc.
- CrowdStrike Holdings, Inc.
- Deloitte Touche Tohmatsu Limited
- Ernst & Young Global Limited
- Google LLC, Mandiant
- International Business Machines Corporation
- Kaspersky Lab
- KPMG International Limited
- Microsoft Corporation
- NCC Group plc
- NTT DATA Corporation
- Optiv Security Inc.
- Palo Alto Networks, Inc.
- PricewaterhouseCoopers International Limited
- Rapid7, Inc.
- Secureworks Corp.
- SentinelOne, Inc.
- Sophos Limited
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Rising Cloud Identity and API Abuse
- 4.2.2 Multi-Cloud and Ephemeral Workload Complexity
- 4.2.3 Regulatory and Cyber-Insurance Response Obligations
- 4.2.4 Shortage of Specialized Cloud Forensics Talent
- 4.2.5 AI-Accelerated Attacker Tradecraft
- 4.2.6 Machine-Readable Evidence and Automated Containment
- 4.3 Market Restraints
- 4.3.1 Evidence Gaps From Logging Misconfiguration
- 4.3.2 Data Sovereignty and Cross-Border Evidence Restrictions
- 4.3.3 Fragmented Tooling and Shared-Responsibility Ambiguity
- 4.3.4 Ephemeral Workload Volatility During Investigation
- 4.4 Impact of Macroeconomic Factors
- 4.4.1 Enterprise Security-Budget Prioritization
- 4.4.2 Cyber-Insurance Pricing and Retention Changes
- 4.4.3 IT Modernization and Cloud Spending Cycles
- 4.5 Value / Supply-Chain Analysis
- 4.6 Regulatory Landscape
- 4.6.1 NIST SP 800-61 and NIST Cybersecurity Framework
- 4.6.2 ISO/IEC 27001, SOC 2 and CIS Controls
- 4.6.3 GDPR, CCPA/CPRA and Regional Privacy Requirements
- 4.6.4 NIS2, DORA and Sectoral ICT-Resilience Rules
- 4.6.5 HIPAA, PCI DSS, SEC Disclosure and Breach-Notification Clocks
- 4.6.6 Evidence Residency, Legal Holds and Cross-Border Transfer
- 4.7 Technological Outlook
- 4.7.1 Cloud-Native Forensics and API-Based Evidence Collection
- 4.7.2 Identity, Entitlement and Token Forensics
- 4.7.3 Container, Kubernetes and Serverless Investigation
- 4.7.4 AI-Assisted Triage and Timeline Reconstruction
- 4.7.5 Automated Isolation, Credential Revocation and Key Rotation
- 4.7.6 Immutable Evidence Lockers and Cryptographic Integrity
- 4.7.7 Cloud Sandboxes, Digital Twins and Deception
- 4.8 Porter's Five Forces Analysis
- 4.8.1 Threat of New Entrants
- 4.8.2 Bargaining Power of Suppliers
- 4.8.3 Bargaining Power of Buyers
- 4.8.4 Threat of Substitutes
- 4.8.5 Competitive Rivalry
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Service Type
- 5.1.1 Investigation and Digital Forensics
- 5.1.2 Containment and Mitigation
- 5.1.3 Remediation and Recovery
- 5.1.4 Managed Detection and Response
- 5.1.5 Other Service Types
- 5.2 By Cloud Environment
- 5.2.1 Public Cloud
- 5.2.2 Private Cloud
- 5.2.3 Hybrid Cloud
- 5.2.4 Multi-Cloud
- 5.3 By Organization Size
- 5.3.1 Large Enterprises
- 5.3.2 Small and Medium Enterprises
- 5.4 By Industry Vertical
- 5.4.1 Government and Public Administration
- 5.4.2 Industrial Manufacturing
- 5.4.3 Retail and E-Commerce
- 5.4.4 Transportation and Logistics
- 5.4.5 Energy and Utilities
- 5.4.6 Oil and Gas
- 5.4.7 IT and Telecommunication
- 5.4.8 Media and Entertainment
- 5.4.9 Education and Research Institutions
- 5.4.10 Healthcare and Life Sciences
- 5.4.11 Banking, Financial Services, and Insurance (BFSI)
- 5.4.12 Other Industry Verticals
- 5.5 By Geography
- 5.5.1 North America
- 5.5.1.1 United States
- 5.5.1.2 Canada
- 5.5.1.3 Mexico
- 5.5.2 South America
- 5.5.2.1 Brazil
- 5.5.2.2 Argentina
- 5.5.2.3 Rest of South America
- 5.5.3 Europe
- 5.5.3.1 Germany
- 5.5.3.2 United Kingdom
- 5.5.3.3 France
- 5.5.3.4 Italy
- 5.5.3.5 Spain
- 5.5.3.6 Rest of Europe
- 5.5.4 Asia-Pacific
- 5.5.4.1 China
- 5.5.4.2 Japan
- 5.5.4.3 India
- 5.5.4.4 South Korea
- 5.5.4.5 Australia
- 5.5.4.6 Rest of Asia-Pacific
- 5.5.5 Middle East
- 5.5.5.1 Saudi Arabia
- 5.5.5.2 United Arab Emirates
- 5.5.5.3 Rest of Middle East
- 5.5.6 Africa
- 5.5.6.1 South Africa
- 5.5.6.2 Nigeria
- 5.5.6.3 Rest of Africa
- 5.5.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global Level Overview, Market Level Overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 Accenture plc
- 6.4.2 Arctic Wolf Networks, Inc.
- 6.4.3 BAE Systems plc
- 6.4.4 Check Point Software Technologies Ltd.
- 6.4.5 Cisco Systems, Inc.
- 6.4.6 CrowdStrike Holdings, Inc.
- 6.4.7 Deloitte Touche Tohmatsu Limited
- 6.4.8 Ernst & Young Global Limited
- 6.4.9 Google LLC, Mandiant
- 6.4.10 International Business Machines Corporation
- 6.4.11 Kaspersky Lab
- 6.4.12 KPMG International Limited
- 6.4.13 Microsoft Corporation
- 6.4.14 NCC Group plc
- 6.4.15 NTT DATA Corporation
- 6.4.16 Optiv Security Inc.
- 6.4.17 Palo Alto Networks, Inc.
- 6.4.18 PricewaterhouseCoopers International Limited
- 6.4.19 Rapid7, Inc.
- 6.4.20 Secureworks Corp.
- 6.4.21 SentinelOne, Inc.
- 6.4.22 Sophos Limited
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-Space and Unmet-Need Assessment
- 7.1.1 Cloud Evidence Residency as a Managed Service
- 7.1.2 Identity-Centric Retainers for Multi-Cloud Estates
- 7.1.3 Incident Response for Containers and Serverless Workloads
- 7.1.4 Outcome-Based Pricing Linked to Containment and Recovery
- 7.1.5 Regional-Language and In-Country Response Coverage
- 7.1.6 Cloud Incident Readiness for Small and Medium Enterprises

 2026-2030年全球事件回應系統市場
 網路安全事件回應服務市場:全球市場預測,2026-2032年
 南美洲事件回應服務:市場佔有率分析、產業趨勢與統計及成長預測(2026-2031 年)事件回應服務:市場佔有率分析、產業趨勢與統計資料、成長預測(2026-2031 年)
 事件回應服務市場報告:按元件、服務類型、安全類型、部署模式、企業規模、最終用戶產業和地區分類(2026-2034 年)
 2026年全球事件回應自動化市場報告2026年全球事件回應市場報告
 事件回應市場:依組件、類型、事件類型、服務、最終用途、國家及地區分類-全球產業分析、市場規模、市場佔有率及2026年至2033年預測
 事件回應系統市場分析及預測(至 2035 年):按類型、產品類型、服務、技術、元件、應用、部署、最終使用者、功能和解決方案分類
 事件回應市場規模、佔有率和成長分析(按組件、服務類型、安全類型、部署類型、組織規模、垂直產業和地區分類)-2026-2033 年產業預測